To allow Users to seamlessly interact with Snowflake Cortex AI directly from Concierge, Metric Insights supports connecting via Model Context Protocol (MCP) Server. Establishing this connection gives Users access to Snowflake's Conversational Analytic and other AI-powered tools, so Users can ask natural language questions about data from Concierge without the need to switch platforms.
Snowflake Managed MCP Server
The benefit of using a Snowflake Managed MCP Server is that it does not require additional setup in Snowflake or deployment of the MCP server in a separate server space.
Here is the diagram of how the connection between Snowflake and Metric Insights work. In this example, Snowflake Cortex has been configured with two Agents, Financial Data and Sales Data. These Agents correlate to their respective Domains in Metric Insights. A User can ask a financial question and Concierge will know to route that question through the correct MCP Server to the specific Domain.
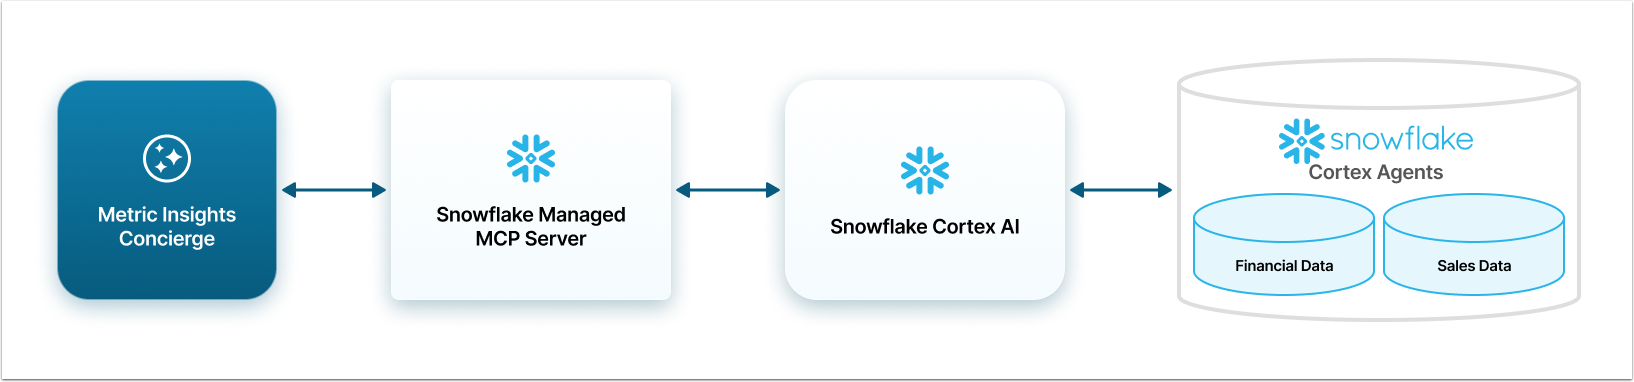
Connecting Concierge to Snowflake Managed MCP Server
Prerequisites
To perform all the steps necessary for connecting Concierge and Snowflake, you need the following:
- Snowflake accounts for all users who will run queries against Snowflake from Concierge must have a default role configured with the required set of permissions:
- USAGE: agent, database, schema, warehouse;
- Additionally, USAGE permission for MCP server and database, schema and all the tables connected to it.
- SELECT on the tables and semantic views (if applicable);
- READ on stages (if applicable);
- USAGE: agent, database, schema, warehouse;
- Microsoft Azure Administrator account for "Service Principal" Auth Type.
- Metric Insights Admin account.
Steps to Connect Concierge and Snowflake
Before starting, decide on the Authentication method. Choose how Concierge will perform authentication when connecting to Snowflake:
- User OAuth: This method is the same as the "Service Account Token" but takes into account the permissions of the User, who makes a query to Concierge. This Auth Type should be used if different users of the Snowflake have different levels of access to data and that difference has to be implemented in their Concierge queries.
- Service Account Token: The Token is requested form Snowflake and inserted into the configuration code automatically. The User only provides credentials to the service account in Snowflake. However, after the Token is expired, the User has to perform Get Token action manually. This Auth Type should be used if OAuth authentication method is used in Snowflake.
- Service Principal: The Token is also requested from Snowflake and automatically inserted into the configuration code by MI, but the user provides Microsoft Entra ID credentials. The Token collected by MI won't expire until the Client Secret value is correct. This Auth Type should be used if your company uses the Microsoft Entra ID identity management platform.
- Defined in configuration: The authentication Token has to be created in Snowflake account and manually inserted into the Concierge configuration code. This Auth Type should be used if the Snowflake has the security model which doesn't include OAuth or has some specific features that require flexible solution.
NOTE: Metric Insights also allows you to connect to Snowflake via REST API calls. For more details, see the Connecting to Snowflake Via REST API article.
Afterward, go through this steps:
- Create and configure Cortex Agents.
- Set the Snowflake Managed MCP Server.
- Collect Connection Information in Snowflake account: Gather credentials for authentication. Create a user Role or configure Misrosoft Entra ID if necessary.
- Configure External Resource in Metric Insights account: Set up Concierge to connect with Snowflake.